NSE5_SDW_AD-7.6 Practice questions
Fortinet NSE 5 - SD-WAN 7.6 Core Administrator
0/5 checked
- free questions
- 5
- with answers
- in the full set
- 141
- question types
- 2
Updated
-
Question 1
Single answer
A branch requires local internet access through two ISP circuits. It has no requirement to reach another site or send internet traffic through a hub.
Branch LAN -- FortiGate -- wan1 -- ISP-A -- Internet
\-- wan2 -- ISP-B -- Internet
Which description of this SD-WAN design is correct?
Show answer
Correct answer
-
B
The ISP circuits are underlays, and a site-to-site VPN overlay is not required for this local internet requirement.
Explanation
The two ISP circuits provide the transport connectivity, so they belong to the underlay. A VPN overlay provides logical connectivity across sites when such connectivity is required. This branch only needs direct internet access (DIA), so configuring two SD-WAN members does not itself require a site-to-site VPN or a hub.
No comments yet. Start the discussion.
-
B
-
Question 2
Multiple answer
An administrator has selected passive mode for an SD-WAN performance SLA. Real TCP application traffic is available, but the matching firewall policy has not yet been prepared for passive WAN health measurement.
Which two policy settings are required to collect passive measurements for that traffic in FortiOS 7.6.3? (Choose two)
Show answer
Correct answer
-
A
Enable passive-wan-health-measurement on the policy that accepts the traffic.
-
C
Set the policy outgoing interface to the appropriate SD-WAN zone.
Explanation
Passive health measurement analyzes real TCP session information. The accepting firewall policy must enable passive-wan-health-measurement, and its outgoing interface must be an SD-WAN zone.
No comments yet. Start the discussion.
-
A
-
Question 3
Single answer
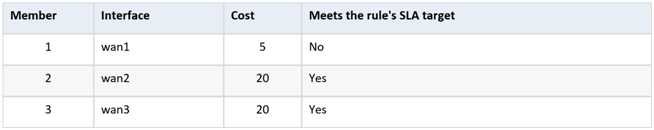
A Lowest Cost (SLA) rule matches a new session. Load balancing is disabled, minimum-sla-meet-members is 1, and priority-members is 3 2 1. All three members are alive and have usable routes. The rule uses one SLA target, and all other rule and zone settings use their defaults.
Which interface should the rule select?
Show answer
Correct answer
-
D
wan3
Explanation
Members 2 and 3 both meet the SLA target, satisfying the minimum count of one qualifying member. Their costs are equal, and load balancing is disabled. The tie is resolved by priority-members, which places member 3 first, so the selected interface is wan3.
No comments yet. Start the discussion.
-
D
-
Question 4
Multiple answer
A Lowest Cost (SLA) rule uses load-balance enable and hash-mode source-ip-based. All listed members are configured in the rule and have usable routes.
There are no additional eligibility restrictions.
Which two statements describe this rule while these conditions remain unchanged? (Choose two)

Show answer
Correct answer
-
A
wan1 and wan2 are in the eligible load-balancing pool despite their different costs.
-
D
The source-ip-based method keeps traffic from a given source IP on the same selected interface under the stated unchanged conditions.
Explanation
With load balancing enabled inside an SLA rule, all usable configured members that meet the target can participate. Both wan1 and wan2 therefore belong to the eligible pool despite their different costs. The source-ip-based hash method sends traffic from a given source IP through the same selected interface while the stated candidate conditions remain unchanged.
No comments yet. Start the discussion.
-
A
-
Question 5
Multiple answer
An administrator is troubleshooting ordinary IPv4 policy-based routes on FortiOS 7.6.3. The packet matches the policy-route address, protocol and port criteria.
Which three statements about completing the forwarding decision are correct? (Choose three)
Show answer
Correct answer
-
A
If only an outgoing interface is configured, FortiGate looks for a gateway using the routing table filtered by that interface.
-
C
If only a gateway is configured, FortiGate looks for an outgoing interface using the routing table filtered by that gateway.
-
D
If the required forwarding information cannot be resolved, FortiGate can continue to the next policy route.
Explanation
A policy route must provide enough information to forward the packet. An interface-only rule needs gateway resolution filtered by that interface, and a gateway-only rule needs interface resolution filtered by that gateway. If the required forwarding information cannot be found, that policy route does not match and FortiGate continues evaluating the list; ordinary routing is used if no policy route matches.
No comments yet. Start the discussion.
-
A
- Unlock to see this question
- Unlock to see this question
136 questions locked
Unlock all 141 NSE5_SDW_AD-7.6 questions
You’ve had 5 for free. The other 136 work just like them: pick an answer, then check it.
- Questions
- 141, each with its answer
- Explanations
- 100% of questions explained
- Formats
- Single answer, Multiple answer
- Version
- 6.0
- Access
- 3 months from purchase
One-time payment
$49.00
Secure checkout